AI security products
Guardian inspects the traffic to your LLM applications at runtime. Guardian Edge masks corporate data in your employees' use of ChatGPT, Claude and Gemini before it leaves the browser. Gözcü and our laboratory produce the Turkish threat data behind these products and our penetration tests.
- Status
- Guardian in beta; both products offered through a pilot programme
- Deployment
- In the cloud or in your own data centre
- Hosting
- Türkiye hosting option
- Frameworks
- OWASP LLM Top 10, MITRE ATLAS, KVKK
Guardian
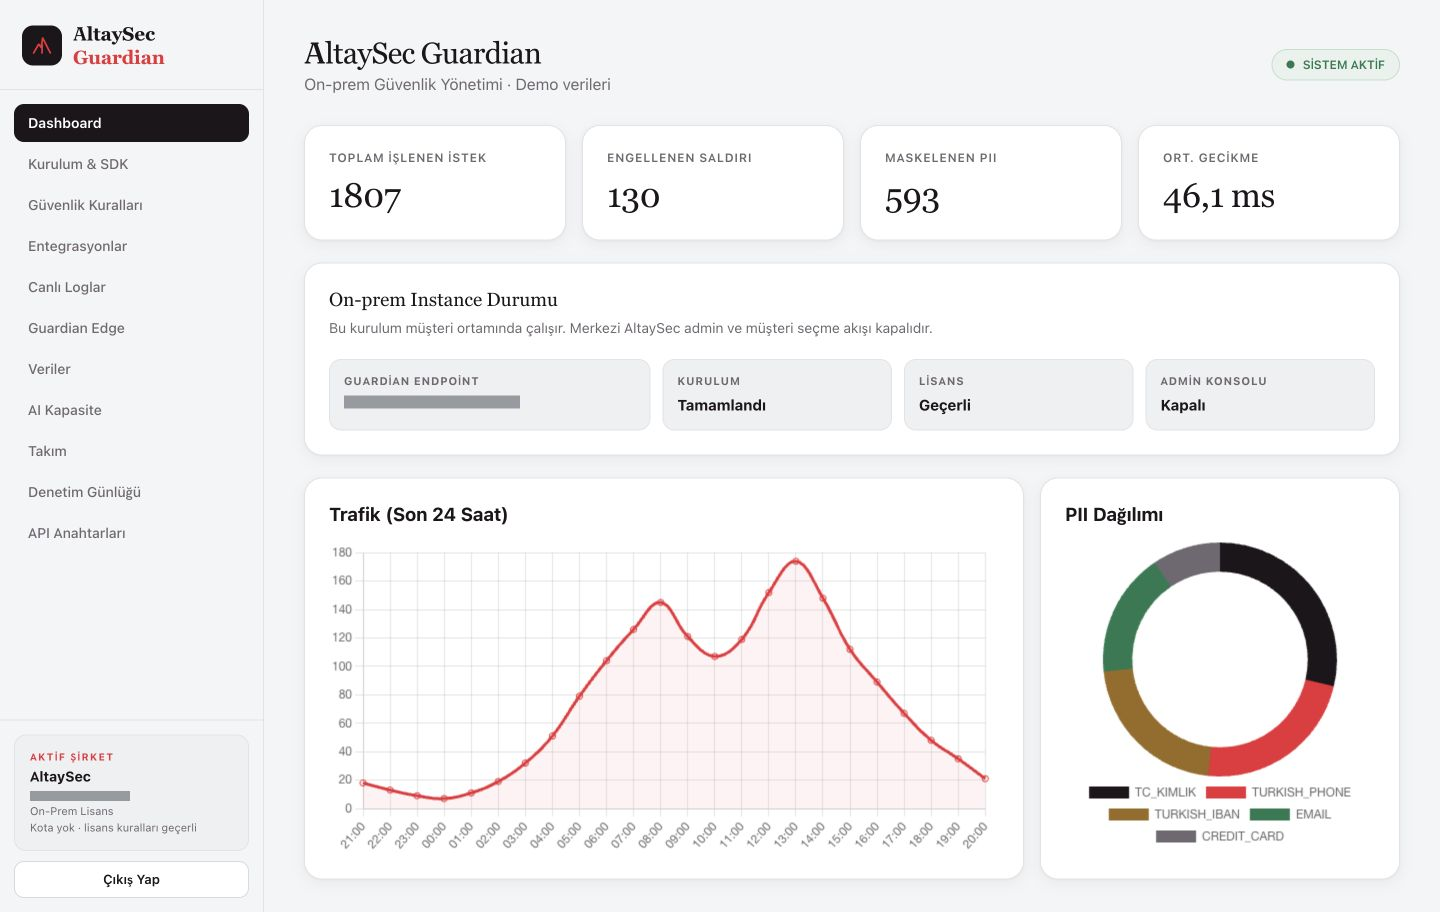
An OpenAI- and Anthropic-compatible security gateway between your application and your model provider. It stops prompt injection, jailbreaks and risky agent actions at runtime, before they reach the model.
Prompt injection and jailbreak prevention
Rule-based checks combined with a fine-tuned mDeBERTa model trained on Turkish evasion techniques.
Masking for 18 Turkish personal data types
National ID numbers (TCKN), IBANs, card numbers and tax IDs, validated with checksums before they are masked.
On-prem container deployment
A Docker Compose setup with a FastAPI web application, PostgreSQL, Redis and local CPU inference, so the data stays inside your network.
Shadow Mode
Guardian inspects prompts and masks data without blocking requests. You measure false positives on your own traffic before you turn on enforcement.
- Protects
- Your own chatbot, RAG and AI agent applications
- Integration
- Only the base_url changes in your SDK
- Coverage
- OWASP LLM01, LLM06, LLM07 and LLM08; KVKK Articles 6 and 12
- Deployment
- Cloud packages, or an on-prem licence in your data centre
- Evaluation
- Free one-week proof of concept
Only the address changes in your application
Your existing SDK code stays as it is. Guardian receives each request, applies your policy and forwards what is allowed to your model provider. Each decision is written to an audit log that can flow to your SIEM.
Guardian is in beta. Cloud demos and applications for an enterprise on-prem proof of concept are open.
# Your existing OpenAI SDK code stays as it isclient = OpenAI(- base_url="https://api.openai.com/v1",+ base_url="https://gw.guardian.altaysec.com.tr/v1", api_key=os.environ["OPENAI_API_KEY"],)What each request passes through
- Injection screening
- Rules and a Turkish-trained classifier look for prompt injection and jailbreak attempts.
- Personal data masking
- National ID numbers, IBANs, card numbers and other personal data are replaced before the model sees them.
- Your policy
- Your organisation's rules decide whether the request is blocked, masked or passed.
- Audit log
- Every decision is recorded and can be sent to your SIEM.
Guardian Edge
A Chrome extension that runs your employees' ChatGPT, Claude and Gemini requests through your Guardian policy. Personal data and API keys are masked before they leave the browser, and a request that breaks the policy is not sent.
Masking before the request leaves
Personal data and secrets are replaced in the browser. Placeholders in the answer are restored on the employee's screen.
Fail-closed by design
If Guardian cannot be reached, the request is not sent. Raw data does not leave the browser.
A limited scope
Guardian Edge is not a keylogger. It inspects only the known chat requests of supported AI sites.
Shadow Mode
Detections are logged without blocking while masking continues, so you can see false positives on your own traffic first.
- Browsers
- Chrome and Chromium-based browsers (Manifest V3)
- Integration
- No code changes; deployed from the panel
- Rollout
- A time-limited pilot link from the panel, then organisation-wide through Chrome Enterprise or MDM with version pinning
- Coverage
- KVKK Articles 6 and 12; visibility into shadow AI use
- Evaluation
- Pilot programme with a free seven-day trial
Gözcü
A Turkish-first library of LLM attacks. Gözcü is research infrastructure that supports our products and testing; it is not sold as a product.
Turkish attack taxonomy
Corporate impersonation, morphological evasion and Turkish-English code-switching.
Standard-mapped records
Every record is mapped to the OWASP LLM and Agentic Top 10, MITRE ATLAS, NIST AI 600-1 and KVKK Article 12.
Gated payloads
Raw attack text is masked in the public repository, and access to it is gated.
Versioned feed
Releases use semantic versioning with sha256 checksums, and consuming systems pin a specific version.
- Status
- Beta, feed version 2.0
- Source
- First-party Turkish data from our laboratory simulations
- Use
- Attack scenarios in our LLM penetration tests; a test and rule source for Guardian development
- Distribution
- Through git
Evaluation and deployment
You evaluate the products in your own environment, with your own traffic. We agree the pilot scope with your security team in writing.
Start in observation mode
In Shadow Mode, Guardian scans requests without blocking them and records its decisions. You turn on blocking once you have seen the false positives in your own traffic.
A controlled browser pilot
Guardian Edge is first installed for a team you choose, through a time-limited link from the panel. It then rolls out across the organisation through Chrome Enterprise or MDM.
Deployment options
Cloud packages, a Türkiye hosting option, and on-prem installation in your own data centre. We can work under an NDA.
For the thinking behind the products, read What is an LLM firewall? and KVKK and personal data in LLM systems.
Let's evaluate Guardian and Guardian Edge in your environment
Define a Shadow Mode scope for Guardian, or a controlled browser pilot for Guardian Edge, together with your security team.